Cybersecurity Analyst resume examples
This page has 12 one-page cybersecurity analyst and security engineer resume examples, from an entry-level cybersecurity specialist triaging SIEM alerts to cloud, application and senior security engineers, a penetration tester, an ISSO, a security architect and an ISSM. Each one is checked against 11,242 US postings from 3,010 employers, and the note under each sample says which tools, frameworks and results it puts first.

Cybersecurity Specialist Resume Example
Why this resume works:
- Triage about 120 Splunk SIEM alerts per shift and escalate confirmed threats to the senior analyst within 15 minutes.
- Run weekly Nessus scans on 900 endpoints and track remediation tickets to closure, lifting patch compliance from 81% to 94%.
- Review IAM access requests and quarterly user access reports for 600 staff, removing 210 stale accounts in the first cycle.

Cybersecurity Analyst Resume Example
Why this resume works:
- Monitor SIEM alerts across 2,300 Windows and Linux hosts and lead incident response, averaging 40 minutes to containment.
- Maintain RMF authorization packages for 6 systems in eMASS, keeping every ATO current through 2 annual assessments.
- Track vulnerability management findings from ACAS scans and drive 310 POA&M items to closure with system owners.
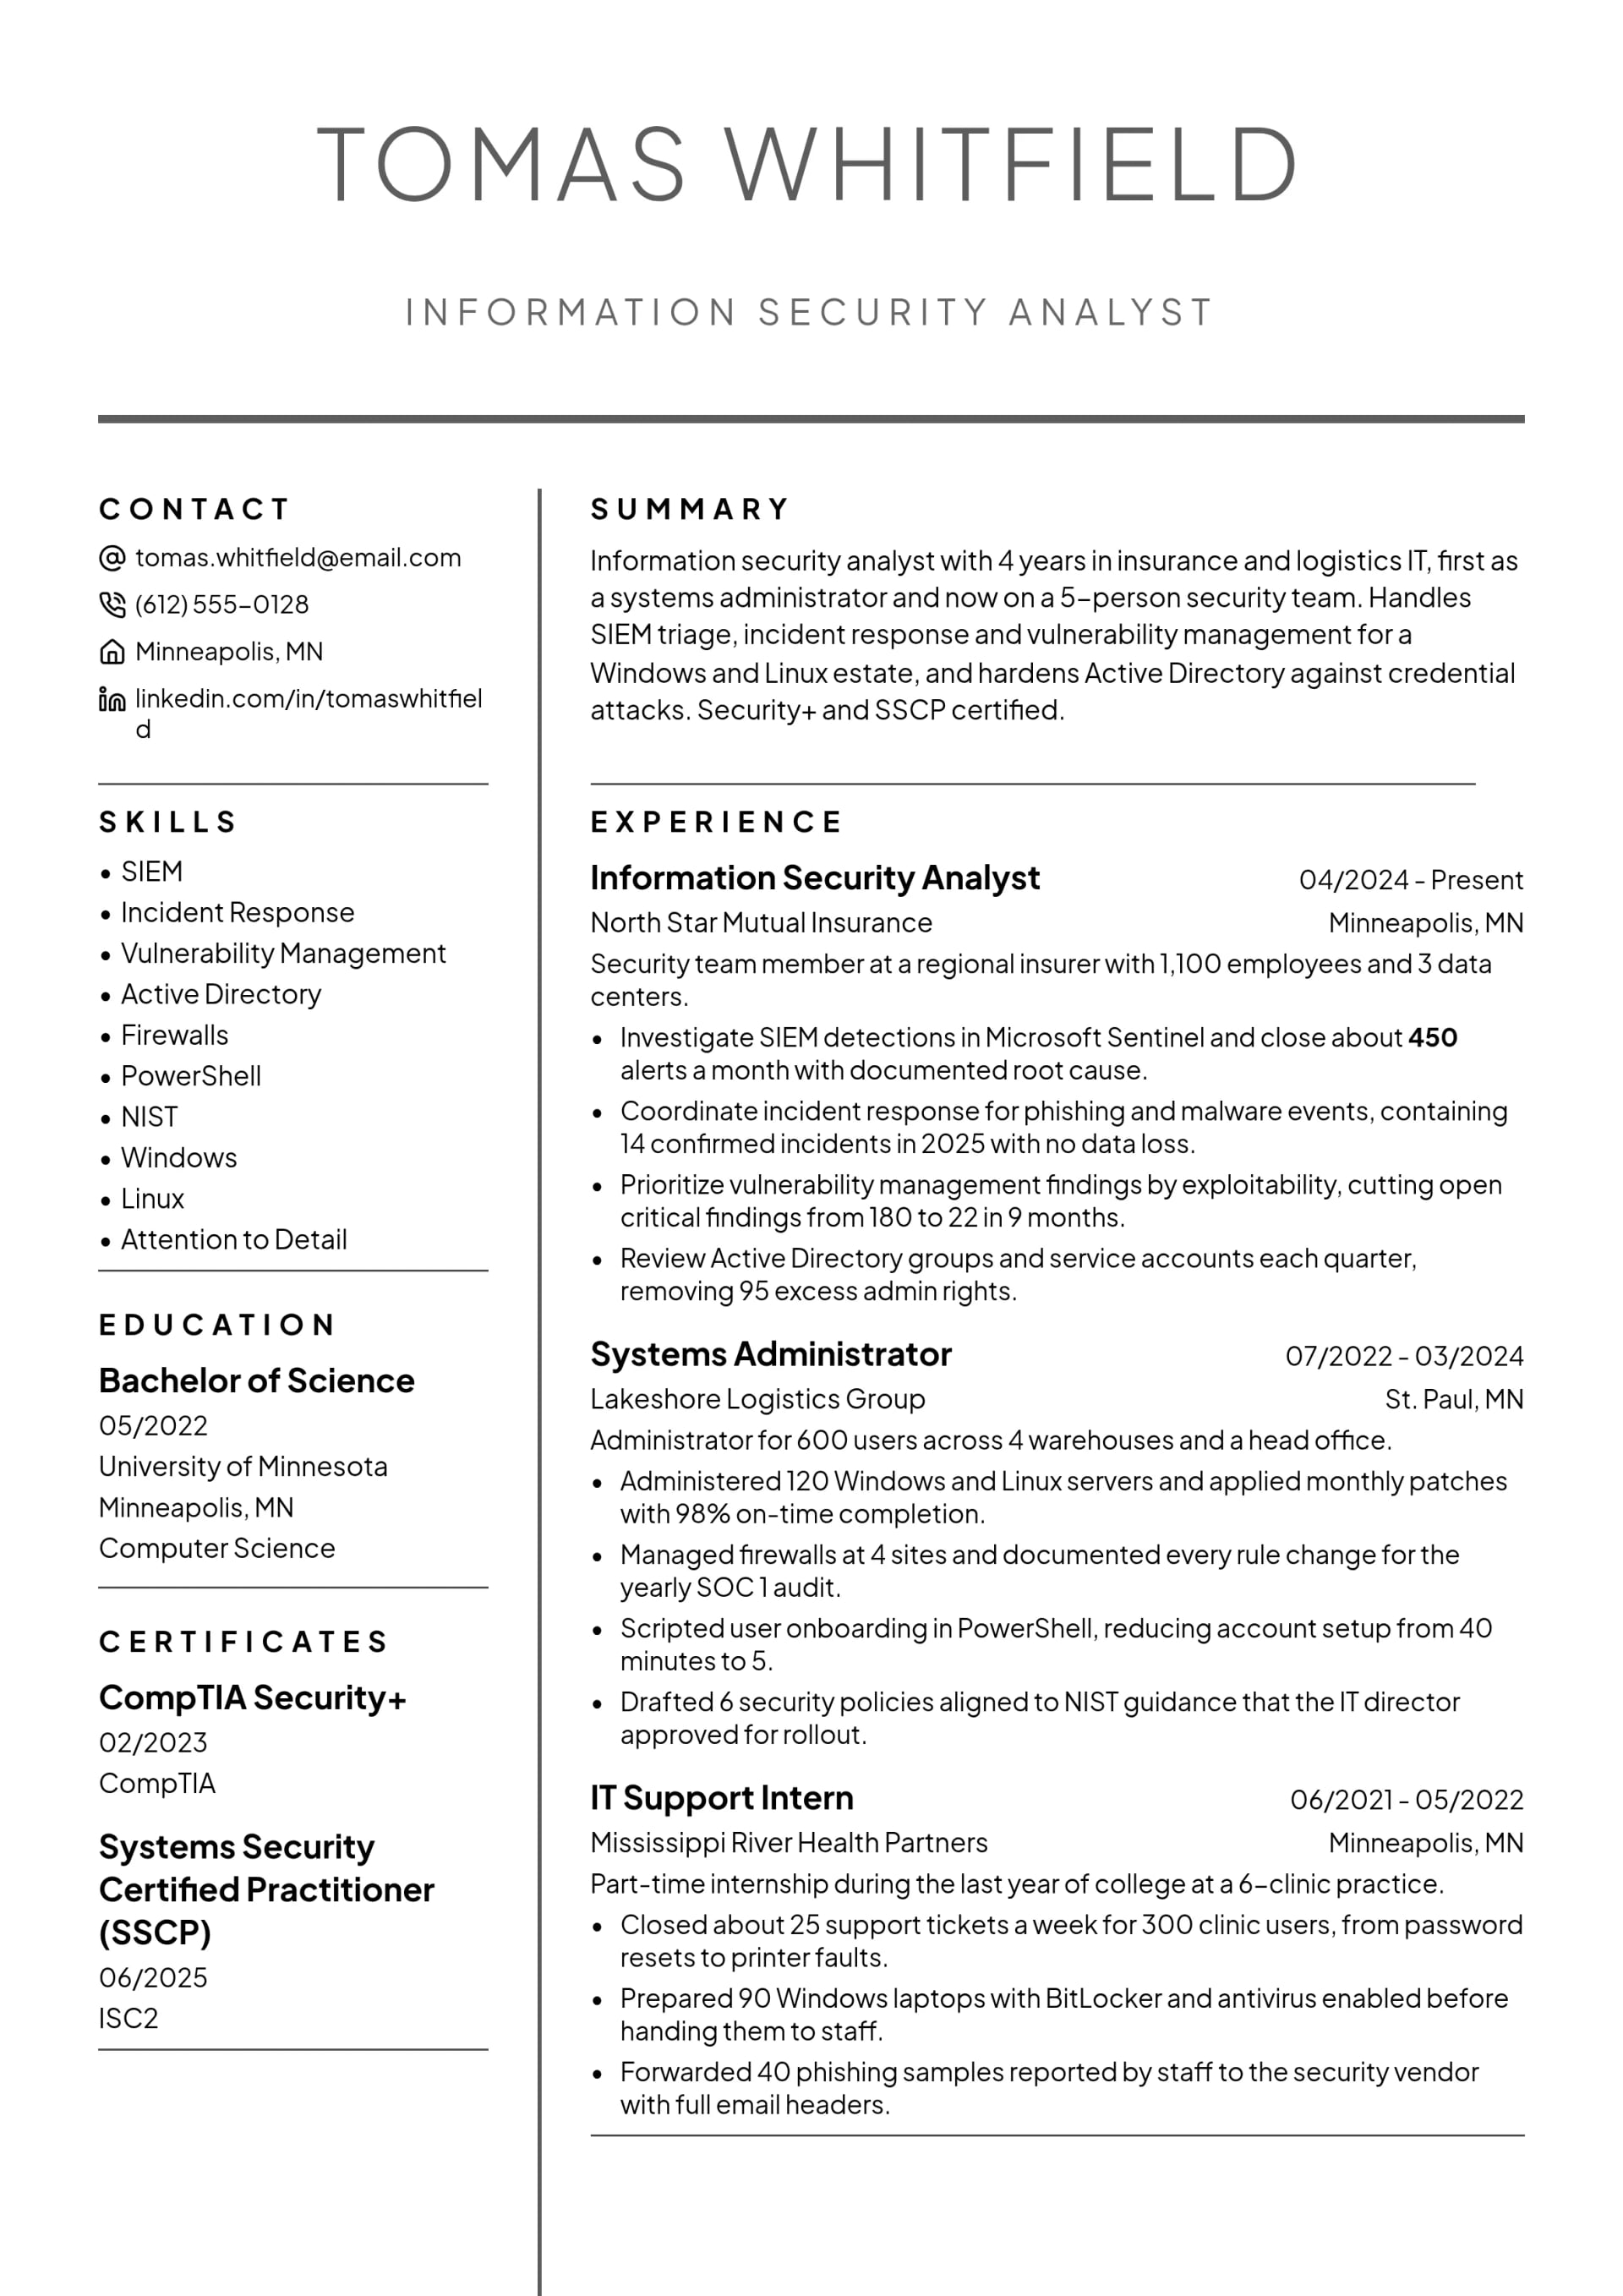
Information Security Analyst Resume Example
Why this resume works:
- Investigate SIEM detections in Microsoft Sentinel and close about 450 alerts a month with documented root cause.
- Coordinate incident response for phishing and malware events, containing 14 confirmed incidents in 2025 with no data loss.
- Prioritize vulnerability management findings by exploitability, cutting open critical findings from 180 to 22 in 9 months.

Security Engineer Resume Example
Why this resume works:
- Build Terraform modules that enforce IAM least privilege across 40 AWS accounts and block public storage by default.
- Tune SIEM detection rules in Splunk, cutting false positives by 60% while adding 35 new detections.
- Run vulnerability management for containers and hosts, keeping critical patch time under 7 days for 1,500 assets.

Cybersecurity Engineer Resume Example
Why this resume works:
- Deploy and maintain SIEM log pipelines for 3,200 endpoints and 40 OT gateways at 99.5% source uptime.
- Manage next-generation firewalls at 18 substations and the corporate core, reviewing 60 rule changes a month.
- Automate vulnerability management reports with Python, giving 30 system owners weekly risk-ranked fix lists.

Cloud Security Engineer Resume Example
Why this resume works:
- Enforce IAM least privilege with Terraform service control policies across 120 AWS accounts.
- Integrate DevSecOps scans for IaC, secrets and images into 85 CI/CD pipelines, blocking 400 risky builds in a year.
- Secure 14 Kubernetes clusters with admission policies and runtime alerts, closing every critical CIS finding.
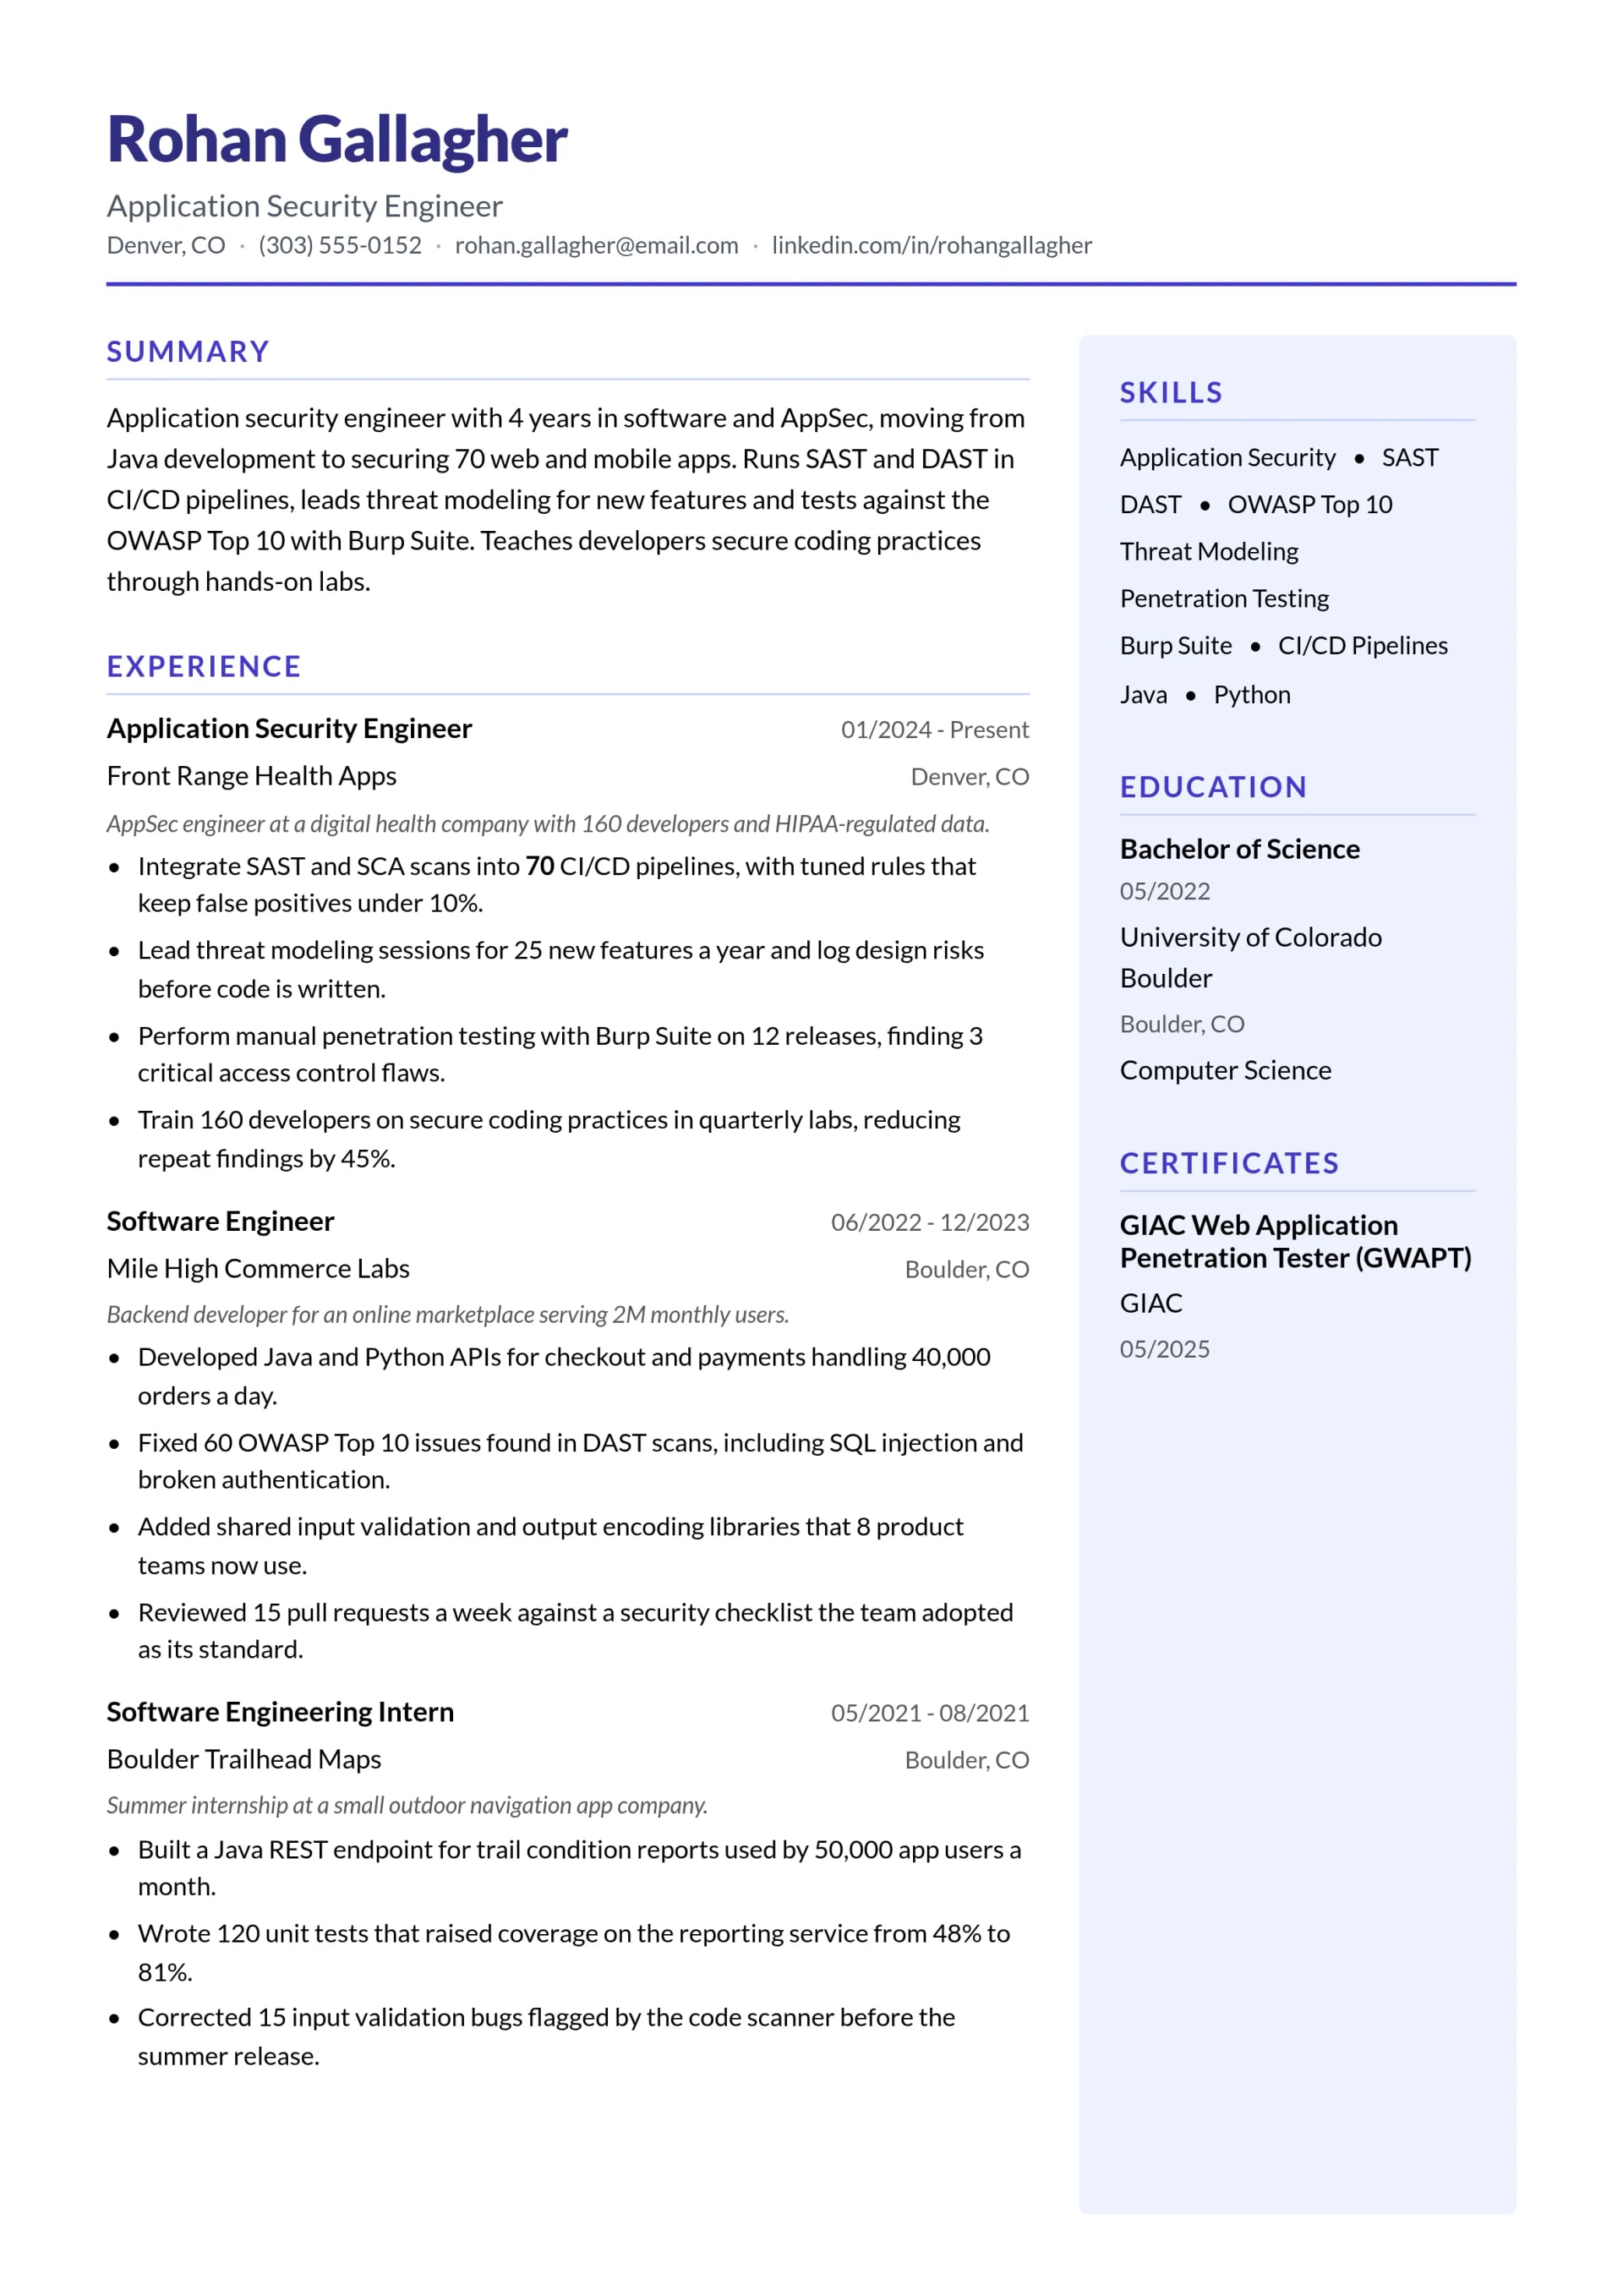
Application Security Engineer Resume Example
Why this resume works:
- Integrate SAST and SCA scans into 70 CI/CD pipelines, with tuned rules that keep false positives under 10%.
- Lead threat modeling sessions for 25 new features a year and log design risks before code is written.
- Perform manual penetration testing with Burp Suite on 12 releases, finding 3 critical access control flaws.

Penetration Tester Resume Example
Why this resume works:
- Deliver 30+ penetration testing engagements a year, from external network tests to full internal assessments.
- Test web apps against the OWASP Top 10 with Burp Suite, reporting 140 findings with clear reproduction steps.
- Run red team exercises with Cobalt Strike and reach domain admin in 9 of 12 internal tests.
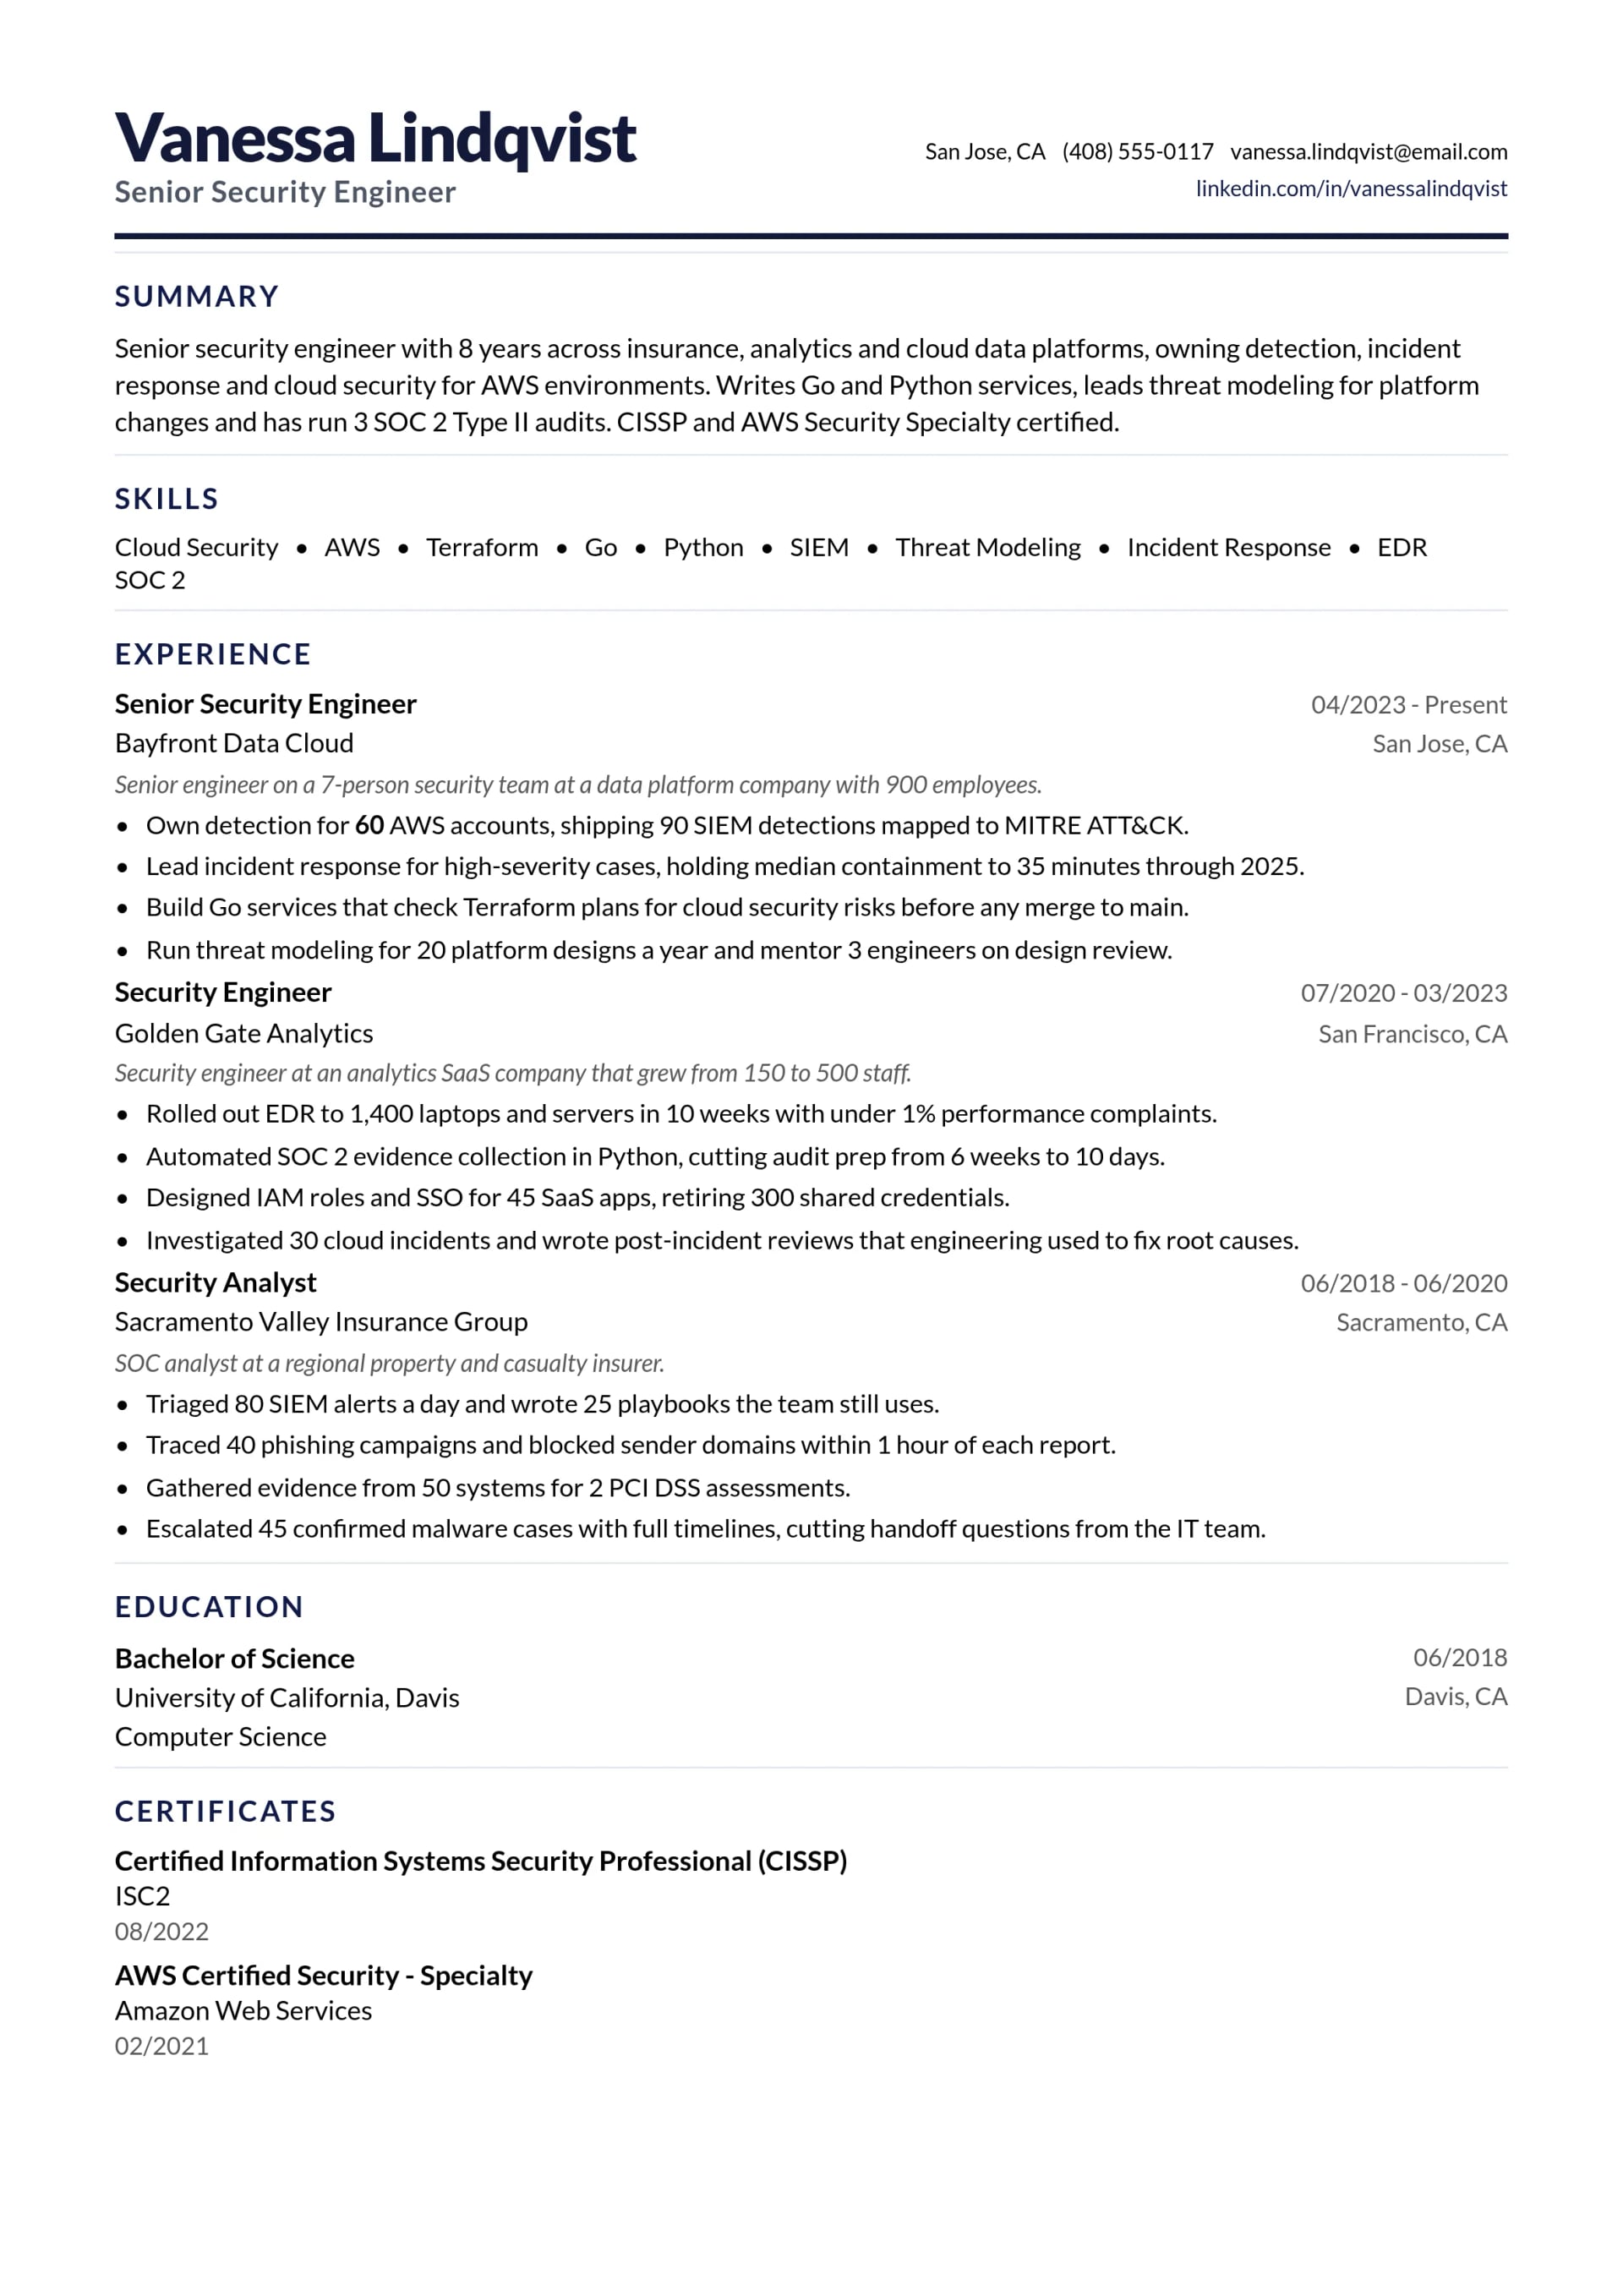
Senior Security Engineer Resume Example
Why this resume works:
- Own detection for 60 AWS accounts, shipping 90 SIEM detections mapped to MITRE ATT&CK.
- Lead incident response for high-severity cases, holding median containment to 35 minutes through 2025.
- Build Go services that check Terraform plans for cloud security risks before any merge to main.
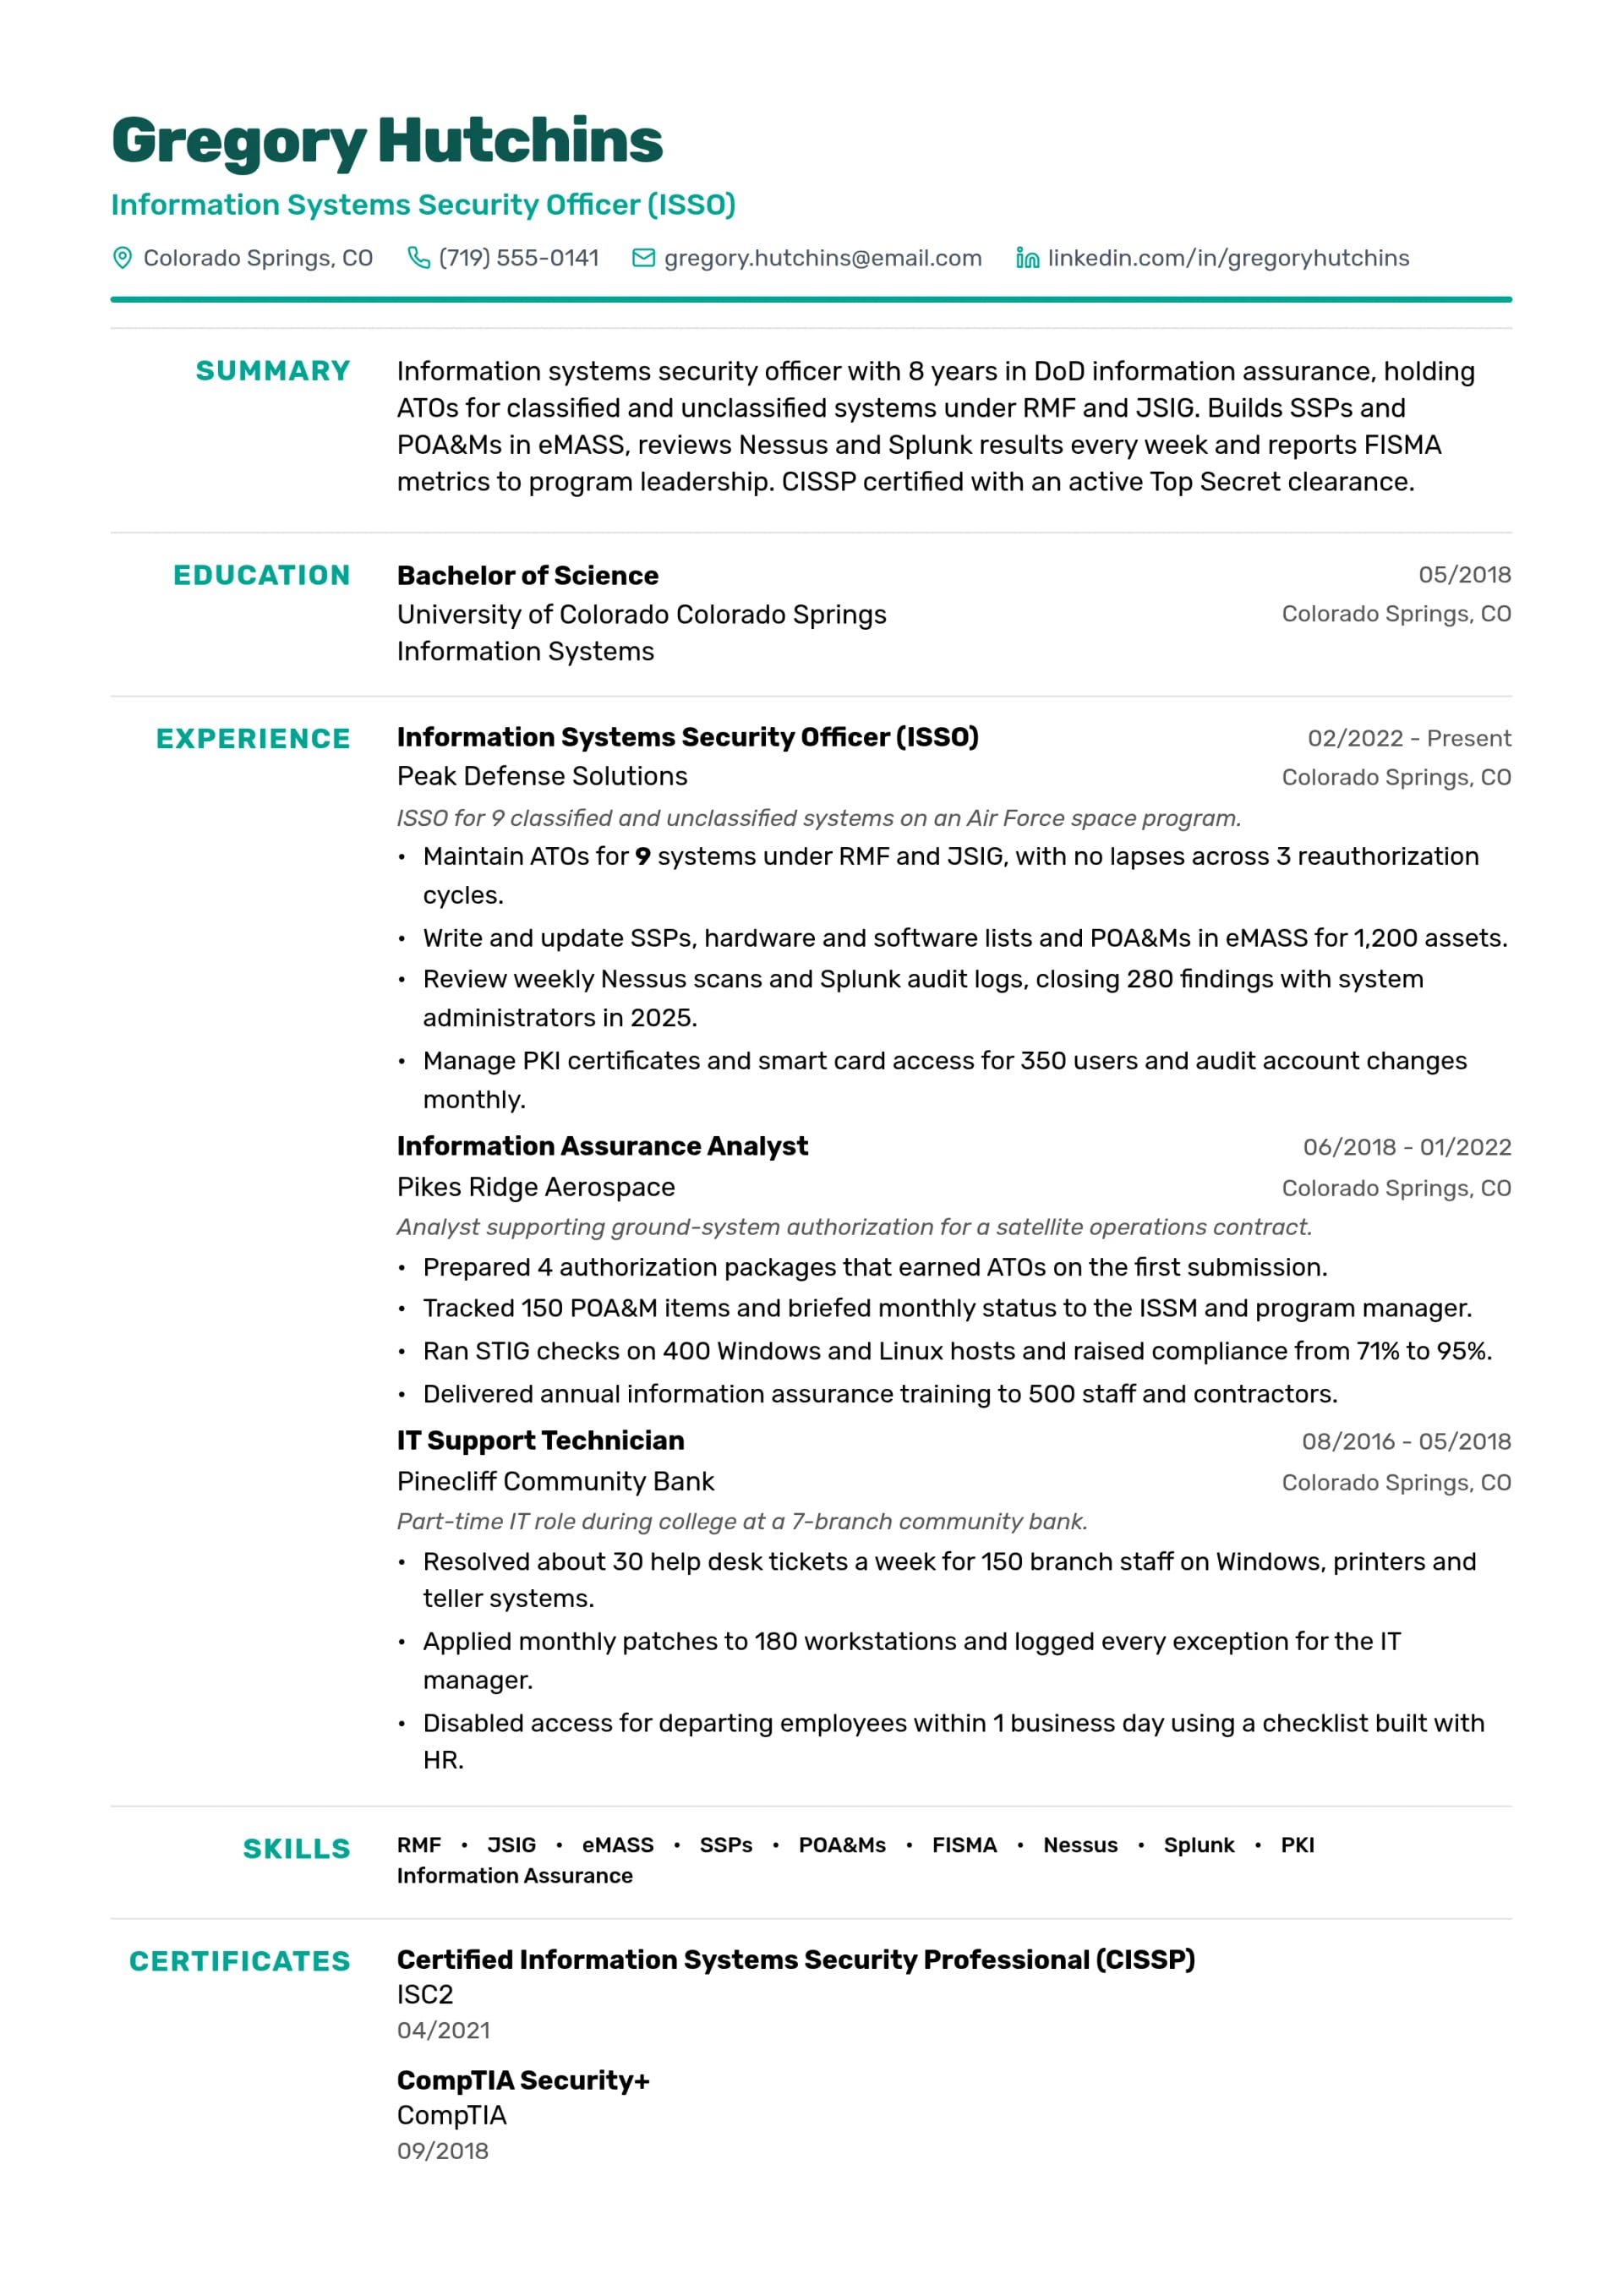
Information Systems Security Officer (ISSO) Resume Example
Why this resume works:
- Maintain ATOs for 9 systems under RMF and JSIG, with no lapses across 3 reauthorization cycles.
- Write and update SSPs, hardware and software lists and POA&Ms in eMASS for 1,200 assets.
- Review weekly Nessus scans and Splunk audit logs, closing 280 findings with system administrators in 2025.

Security Architect Resume Example
Why this resume works:
- Set the security architecture for the AWS and Azure landing zones that now host 220 applications.
- Lead threat modeling for 30 major programs a year through design reviews at the architecture board.
- Map 110 controls to NIST CSF and present the target-state roadmap to the CIO and audit committee.
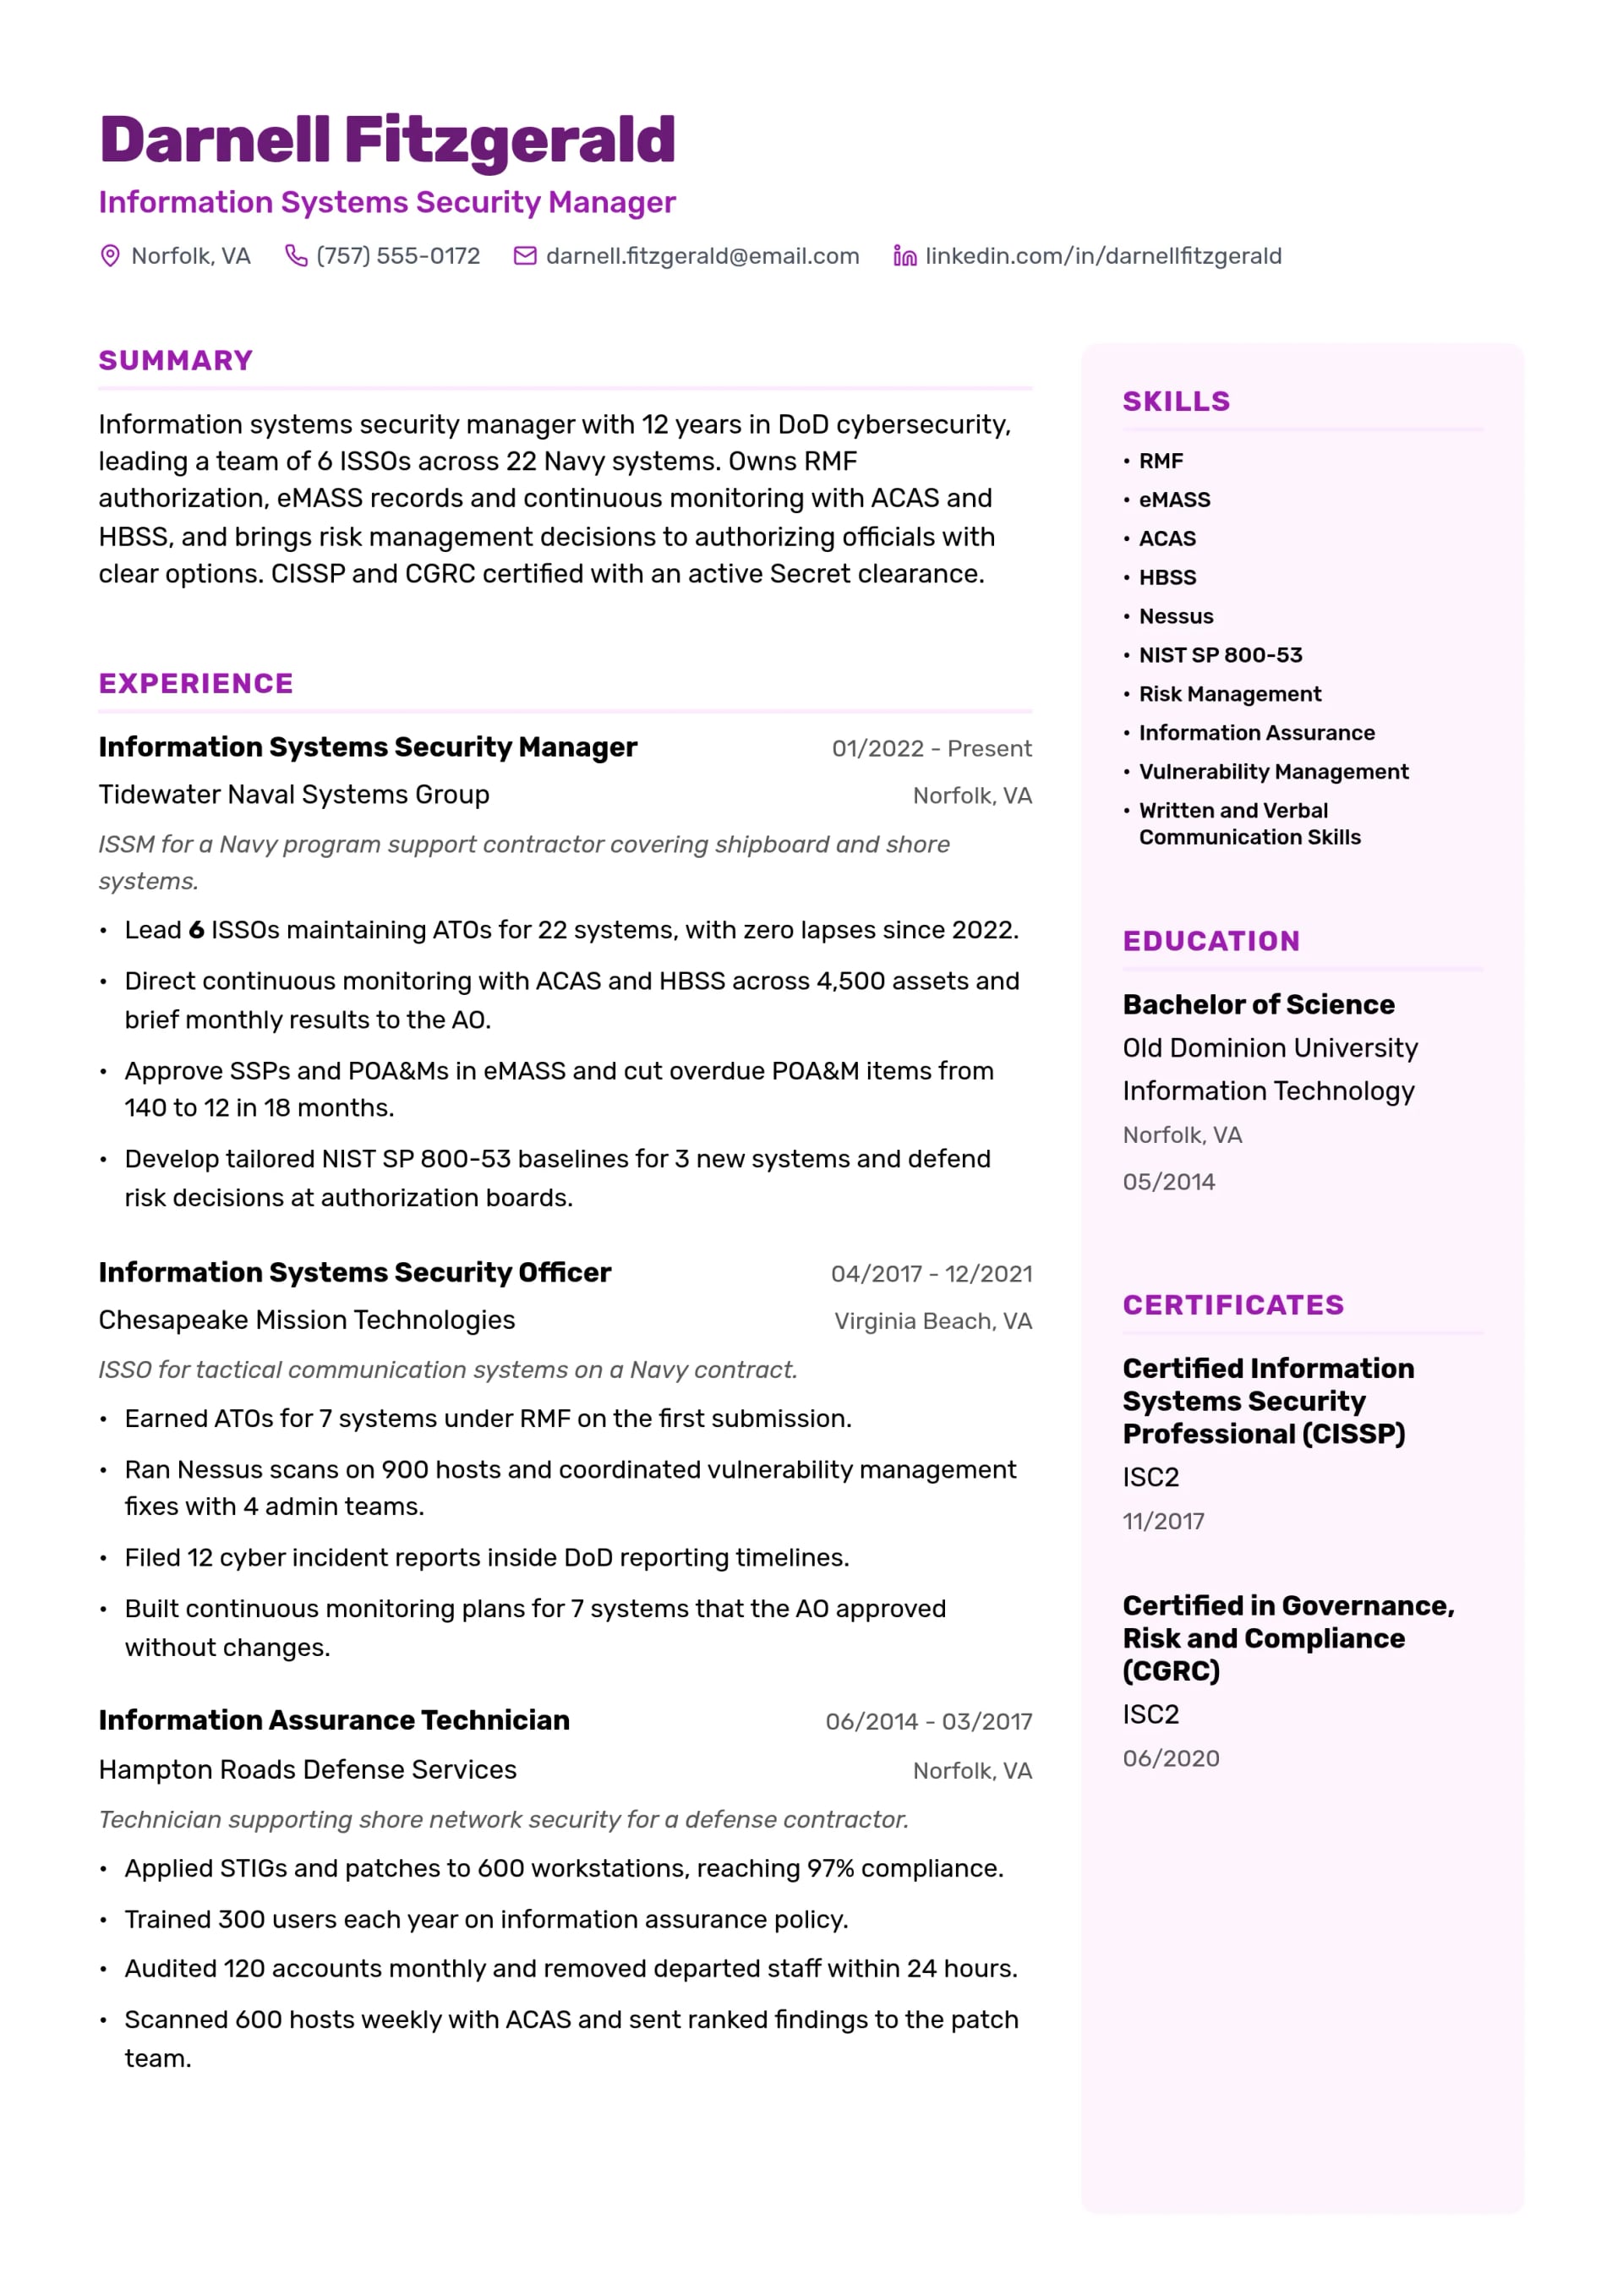
Information Systems Security Manager Resume Example
Why this resume works:
- Lead 6 ISSOs maintaining ATOs for 22 systems, with zero lapses since 2022.
- Direct continuous monitoring with ACAS and HBSS across 4,500 assets and brief monthly results to the AO.
- Approve SSPs and POA&Ms in eMASS and cut overdue POA&M items from 140 to 12 in 18 months.
What employers ask for in cybersecurity analyst job postings
Cybersecurity Analyst job postings in the US, October 2026
- 11,242
- active US job postings
- 3,010
- employers hiring
- 5 yr
- median experience asked
- 7%
- ask for 1 year or less
Technical skills and tools employers name
| Skill | Share of postings |
|---|---|
| siem | 13% |
| python | 26% |
| vulnerability management | 9% |
| aws | 16% |
| cybersecurity | 10% |
| incident response | 8% |
| powershell | 10% |
| azure | 13% |
| nist | 8% |
| cloud security | 8% |
Make sure your resume shows
- 5+ years of cybersecurity, infrastructure or security engineering experience (45% of employers)
- Bachelor's degree in computer science, IT, cybersecurity or a related field (40% of employers)
- CISSP, CCSP, Security+ or an equal security certification (23% of employers)
- Strong analytical and problem-solving skills (22% of employers)
- Knowledge of information security practice and risk management (20% of employers)
- Clear written and spoken findings for technical and executive audiences (18% of employers)
- Scripting or automation in Python, PowerShell or Bash (14% of employers)
- Cloud security experience on AWS, Azure or Google Cloud (10% of employers)
Duties to build your bullet points around
What employers write most often under responsibilities. Show each one with a result (numbers, scale, outcome), not a copy of the duty.
- Respond to security incidents, investigate impact and build mitigations (20%)
- Run vulnerability scans, track remediation and document findings (11%)
- Write and maintain security policies, standards and procedures (9%)
- Support security audits, assessments and compliance reviews (7%)
- Work with engineering, infrastructure and product teams to build security in (7%)
- Carry out security reviews, vulnerability assessments and risk analyses (5%)
The examples on this page, in job postings
| Example | US postings | Median years asked | Skills that set this role apart |
|---|---|---|---|
| Cybersecurity Specialist | 94 | 5 | – |
| Cybersecurity Analyst | 178 | 3 | – |
| Information Security Analyst | 133 | 2 | – |
| Security Engineer | 592 | 5 | security engineering |
| Cybersecurity Engineer | 337 | 4 | cybersecurity engineering |
| Cloud Security Engineer | 106 | 5 | – |
| Application Security Engineer | 106 | 4 | – |
| Penetration Tester | 106 | 3 | – |
| Senior Security Engineer | 244 | 5 | – |
| Information Systems Security Officer (ISSO) | 238 | 4 | rmf, acas, emass, communication protocols |
| Security Architect | 185 | 5 | – |
| Information Systems Security Manager | 63 | 4 | – |
Which job title to put on your resume: the titles employers use most, so recruiters and applicant tracking systems search for them: Security Engineer (348 employers), Cybersecurity Engineer (178 employers), Senior Security Engineer (135 employers), Cyber Security (113 employers), Cyber Security Engineer (111 employers).
Source: Owlapply analysis of active US job postings, October 2026. Requirements and duties are grouped by meaning from the postings' own bullet lists and counted once per employer.
Advertised pay, experience and the skills employers ask for: Cybersecurity Analyst pay and requirements.
Check your cybersecurity analyst resume against a real job posting
- Paste a cybersecurity analyst job posting into the job match score tool to see which of its skills your resume is missing.
- Upload your resume to the ATS resume checker to read the text an applicant tracking system gets from it.
Cybersecurity Analyst resume sample (text you can copy)
This is the text of the Cybersecurity Analyst example above. Paste it into the resume builder and replace the details with your own.
How to write a cybersecurity analyst resume
Write a cybersecurity analyst resume summary
- Name your lane in the first line: SOC and incident response, vulnerability management, GRC and RMF, cloud security, AppSec or offensive testing.
- Give the size of what you protect, such as hosts, endpoints, cloud accounts or systems under ATO, so a hiring manager can judge scale.
- List the certifications and clearance the posting asks for, such as Security+, CySA+, CISSP or OSCP, and a Secret or Top Secret clearance for DoD work.
- Name the main tools and frameworks you use daily, such as Splunk or Sentinel, NIST SP 800-53 or MITRE ATT&CK, instead of a general security line.
Write cybersecurity analyst experience bullets
- For SOC and incident response work, show alert volume, escalation time and time to containment.
- For vulnerability management, show the assets scanned and the before-and-after count of open critical findings or patch compliance.
- For GRC, RMF and ISSO work, count the systems you hold ATOs for, the POA&M items you closed and the audits you passed.
- For engineering and automation, show what your Python, PowerShell or Terraform work changed: hours saved, false positives cut or risky changes blocked.
Pick the skills for a cybersecurity analyst resume
- Python appears in about 26% of postings, AWS in about 16%, Azure in about 13% and PowerShell in about 10%; list the ones you use and show each in a bullet.
- SIEM (about 13%), vulnerability management (about 9%) and NIST, incident response and cloud security (about 8% each) are far more common here than in other jobs; name the product too, such as Splunk, Sentinel, Nessus or CrowdStrike.
- Communication shows up in about 33% of postings and analytical skills in about 16%; prove them with incident reports, executive briefings or audit write-ups rather than listing them alone.
Do's and don'ts
Do this
- Put each certification in its own section with the full name, such as CompTIA Security+ or CISSP.
- Match the posting's framework words exactly, such as NIST SP 800-53, RMF, eMASS, ISO 27001 or SOC 2.
- Give every bullet a number: alerts, hosts, findings closed, minutes to containment or accounts covered.
- State your clearance level and whether it is active when you apply for government or defense roles.
Avoid this
- Don't list dozens of tools you only touched in a lab; employers check them in the interview.
- Don't write "monitored the network" without saying which tool, how many assets and what you found.
- Don't mix offensive and defensive goals in one summary; a pen tester resume and a SOC resume read as different jobs.
- Don't include client names, internal IPs or details of open vulnerabilities from past employers.
Related resume examples
- Sales Engineer
- Systems Administrator
- Solutions Architect
- IT Manager
- DevOps Engineer
- Engineering Manager
- Network Engineer
- AI Engineer